ISC2’s AI security outline is a role design signal, not a finished credential
The pilot exam spans six domains from governance to incident response and is not expected to become operational until 2027. Employers can use the outline to test role coverage without treating it as proof of competence.
What happened
ISC2 released the pilot exam outline for a proposed AI security certification on 26 October after job-task analysis, workshops and input from more than 9,500 volunteers across over 150 countries.
Why it matters
The outline makes AI security look like a cross-lifecycle profession, but the pilot has not yet validated the exam and a future credential should not substitute for demonstrated work in a specific operating environment.
A proposed body of practice
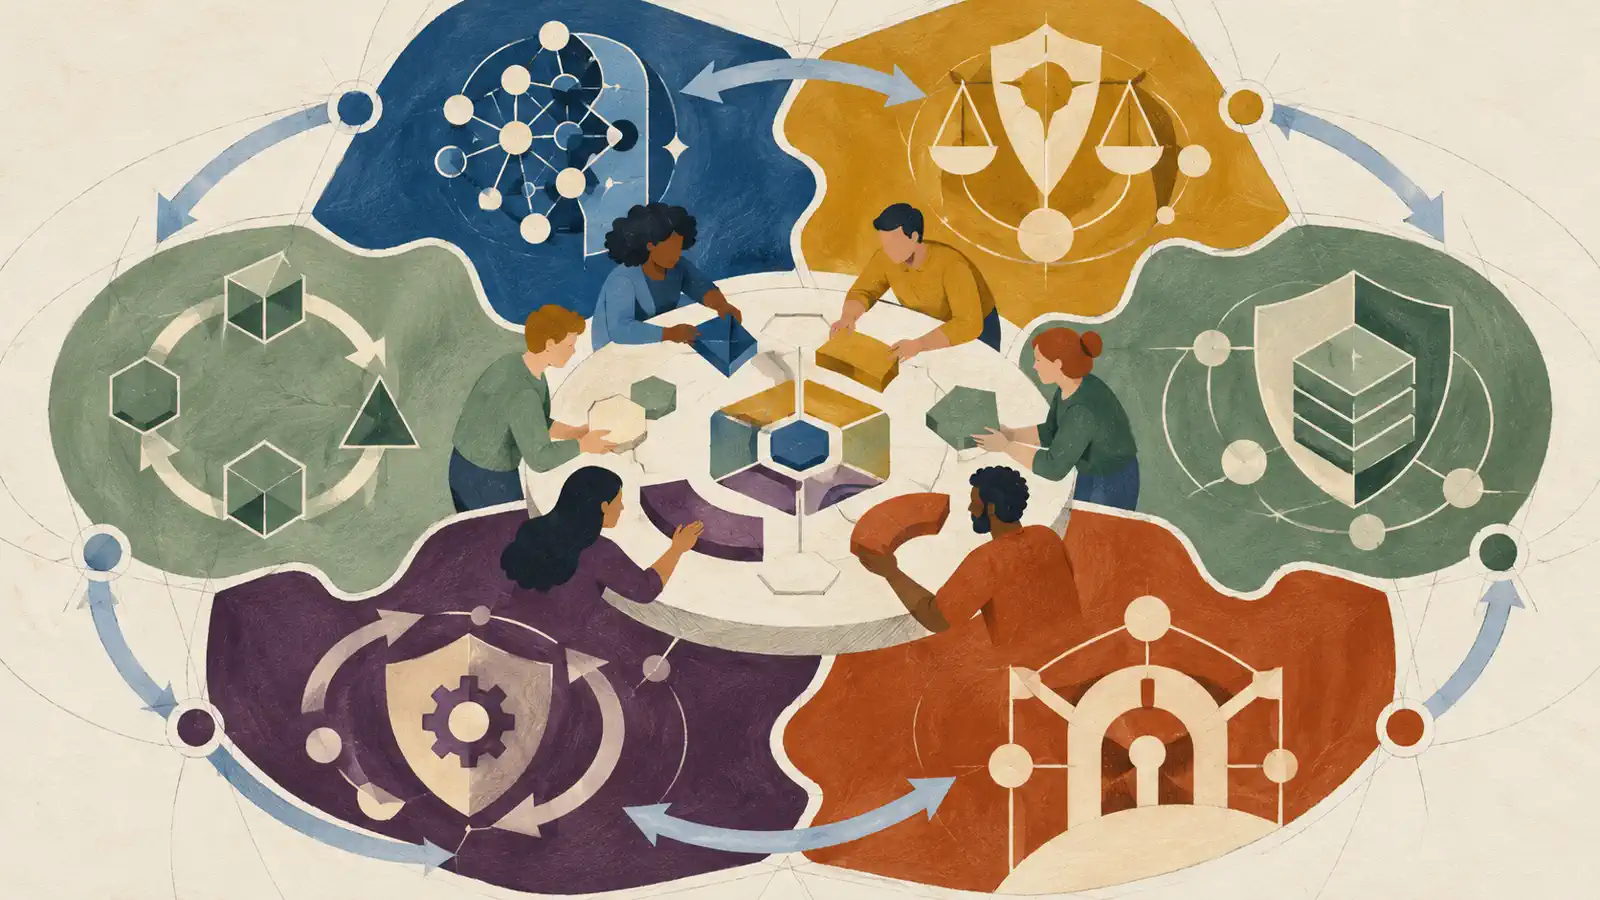
ISC2’s programme update says its proposed AI security certification has entered the pilot stage. The outline spans six domains: AI concepts and security fundamentals; governance, ethics, risk and compliance; data, privacy and model security; secure architecture, engineering and identity; operations and incident response; and threats, testing and lifecycle management.
ISC2 reports that more than 9,500 volunteers from over 150 countries expressed interest, with more than 1,100 responses to its job-task-analysis survey. Workshops were held in Alexandria, London and Singapore, followed by item development and review. Approximately 3,000 qualified volunteers are expected to take the pilot exam from mid-December through late January. The certification is not expected to become operational until 2027, subject to successful validation and approval.
Those details make the outline a useful signal about how a professional association is organising AI security work. They do not show that the exam reliably predicts workplace performance, that the volunteer pool represents every region or sector, or that a candidate can earn the operational credential today.
The outline crosses organisational boundaries
Intrinsec’s independent review notes that data and model security, secure architecture and identity, and operations and incident response account for 56% of the proposed weighting. It also emphasises that the scope extends beyond generative AI to machine learning, infrastructure and the full lifecycle. Intrinsec is a training provider, so its interpretation has commercial context and is not an independent psychometric validation.
The important workforce signal is breadth. AI security is not only prompt injection or model testing. The outline connects governance, privacy, data provenance, architecture, identity, operations, response, assurance and collaboration. One employee may not own all of those decisions even if one examination samples them.
Turn domains into a team coverage map
Map the six domains to decisions in the current operating model. For each decision, identify the accountable role, supporting roles, required evidence and escalation route. Then mark whether the capability is needed to design, operate, assure or govern a system. Gaps may call for hiring, development, a specialist or a clearer handoff—not necessarily one new job title.
Use work samples alongside the outline. Ask candidates or employees to threat-model a representative AI workflow, trace an identity and data boundary, evaluate a third-party control, design an incident response or explain an uncertain regulatory requirement. Score reasoning, evidence use, escalation and ability to recognise when deeper expertise is needed. Do not infer production authority from exam preparation alone.
Preserve the distinction between a certificate, a certification pilot and an operational certification. ISC2 itself distinguishes learning products from a professional credential with continuing requirements. Procurement and HR systems should not mark the pilot as an earned certification or automatically require it before the scheme exists.
Treat the proposed weights as sampling choices, not a universal allocation of work. A regulated model operator, a software supplier and an incident-response provider can need different depth even when they share the same six headings. Local risk and operating responsibility should still determine development priorities.
Wait for validation evidence
When pilot results become available, ask what was measured: reliability, pass-standard setting, item performance, fairness, security and evidence that domains reflect job tasks. Review experience requirements and renewal rules when final, and check access constraints such as language, testing location and cost. A global label can still create regional barriers.
This complements the CompTIA AI safety readiness assessment: training completion and credential status should feed a broader work-evidence record rather than replace it.
Decision rule
Use the pilot outline now as a team coverage checklist, not as a hiring mandate or competence claim. Do not add the proposed credential to a required-field filter until it is operational and its validation evidence is reviewed. Even then, pair it with representative work samples and role-specific authorization.