A unified AI workspace moves the control boundary into the conversation
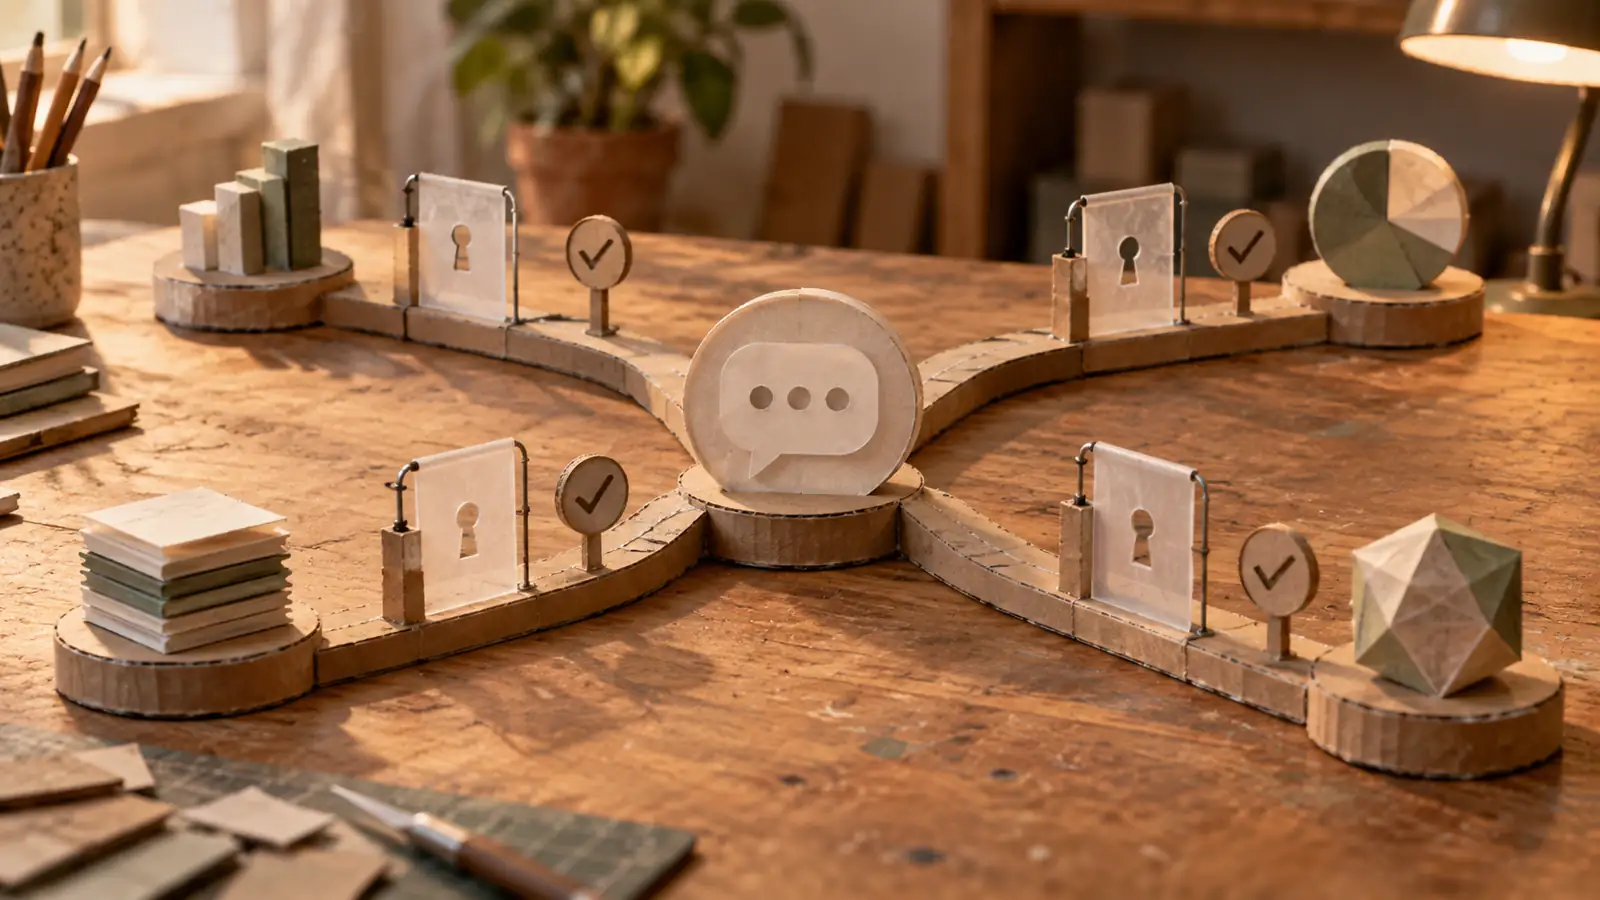
Bringing chat, Cowork and document creation into one interface removes friction for users. It also means a conversation can cross from advice into file access, state-changing work and export without a visible application boundary.
What happened
Anthropic announced a unified Claude interface and beta Docs and Slides tools, with the system selecting capabilities and exporting work into common document formats.
Why it matters
When one conversation can read files, create deliverables and trigger actions, governance must follow the action and data—not the product tab a user sees.
Reuters reports that Anthropic is bringing Claude’s chat, Cowork and other capabilities into one interface that selects the appropriate mode. The Verge’s account describes beta Docs and Slides tools and exports to formats such as Word or Google Docs, PowerPoint and PDF. Initial availability begins with Pro and Max users before Team and Free plans.
This is product scope, not evidence of productivity, accuracy or security. Features and controls may change during beta. The important operating change is that the visible boundary between asking, creating, accessing files and exporting becomes less obvious to the user.
Classify the action behind the conversation
A chat prompt can be low risk when it asks for a generic explanation. The same surface becomes materially different when it reads a local folder, edits a document, combines customer information, writes a file or sends content into another system. Policy attached only to the product name will miss those transitions.
Create an action catalogue: advise, retrieve, transform, create, export and execute. For each action, define permitted data, approved destinations, required review, logging and who can grant access. The interface may select a capability automatically, but organisational approval should not be inferred from that selection.
Anthropic’s Cowork safety guidance tells users to grant explicit folder permissions, avoid sensitive files and monitor actions. Those are useful precautions. They also show why permission is not a one-time setup detail. A broad folder grant can expose unrelated material, and a benign request can produce an export containing data that were only needed temporarily.
Put gates at permission and export
The first gate should limit scope: use task-specific folders or copies, short-lived access and the minimum connectors needed. The second should sit before a consequential change or external export. The user should see the destination, data classes, files and requested action, then approve or stop it. High-risk workflows need a second reviewer or an alternative controlled path.
Logs should connect the conversation to the selected capability, permission grants, files read, transformations, output version, export target and human approval. Otherwise, an incident review sees a polished document without the context needed to explain how it was assembled.
The strongest counterargument is that extra gates erase the value of a unified workspace. Controls can indeed become theatre if every harmless step needs approval. Risk-tier the actions instead. Generic drafting may need ordinary review; access to regulated data, state-changing work or external transmission requires stronger evidence. Measure interruptions, false blocks, corrected outputs and completed work, not the number of warnings displayed.
Separate Reuters reporting describes enterprise restrictions motivated by data concerns. It does not test Claude’s new interface and cannot show that it is unsafe. It does show that data boundaries remain a live adoption constraint, so a smoother interface does not remove the need for enforceable controls.
Procurement and identity design matter too. Plan-level availability is not the same as organisational readiness. Before expansion, confirm which administrator can disable a capability, whether access follows group membership, how departing users lose grants, and which logs the organisation can retain. A manual checklist cannot compensate for an entitlement that remains broader than the approved task.
The Skills Atlas can identify capability needs in data judgement, tool use, verification and escalation. The immediate decision is to govern the action graph: approve data access narrowly, require a visible gate before consequential export or execution, and preserve a trace from request to final artefact.
A bounded pilot
Choose one document workflow with non-sensitive or well-classified data. Predefine allowed folders, output formats, destinations, review criteria and rollback. Test whether users can identify when the system changes mode, whether permission prompts match the actual scope and whether the exported file preserves required attribution. Expand only after the trace is complete and exceptions have an accountable owner.